CyberDefenders is an independently funded nonprofit project..
Donate
Merritt College Cybersecurity Department
At the Merritt College Cybersecurity Job Fair & Employer Day, students walked up, scanned a QR code and
tried to hack an AI in about 15 minutes. Sign up, learn on TryHackMe, hack our AI Labs, compete in a prompt injection CTF.
It's a wrap! R-Building (Newton/Seale Lounge), Merritt College, Oakland.
Both AI Labs and the CTF are open source on GitHub.
Why an AI Village
Almost every employer at the fair is putting AI into something: a chatbot, a help desk, an email assistant. Very few of our
students have ever tried to break one. Prompt injection is the number one risk on the OWASP Top 10 for LLM applications, and you
don't need to write any code to try it. You just need words. That makes it a great first hack for someone new to security, and a
good story to tell at the next employer table.
The name and the hands-on format come from the AI Village community and their open
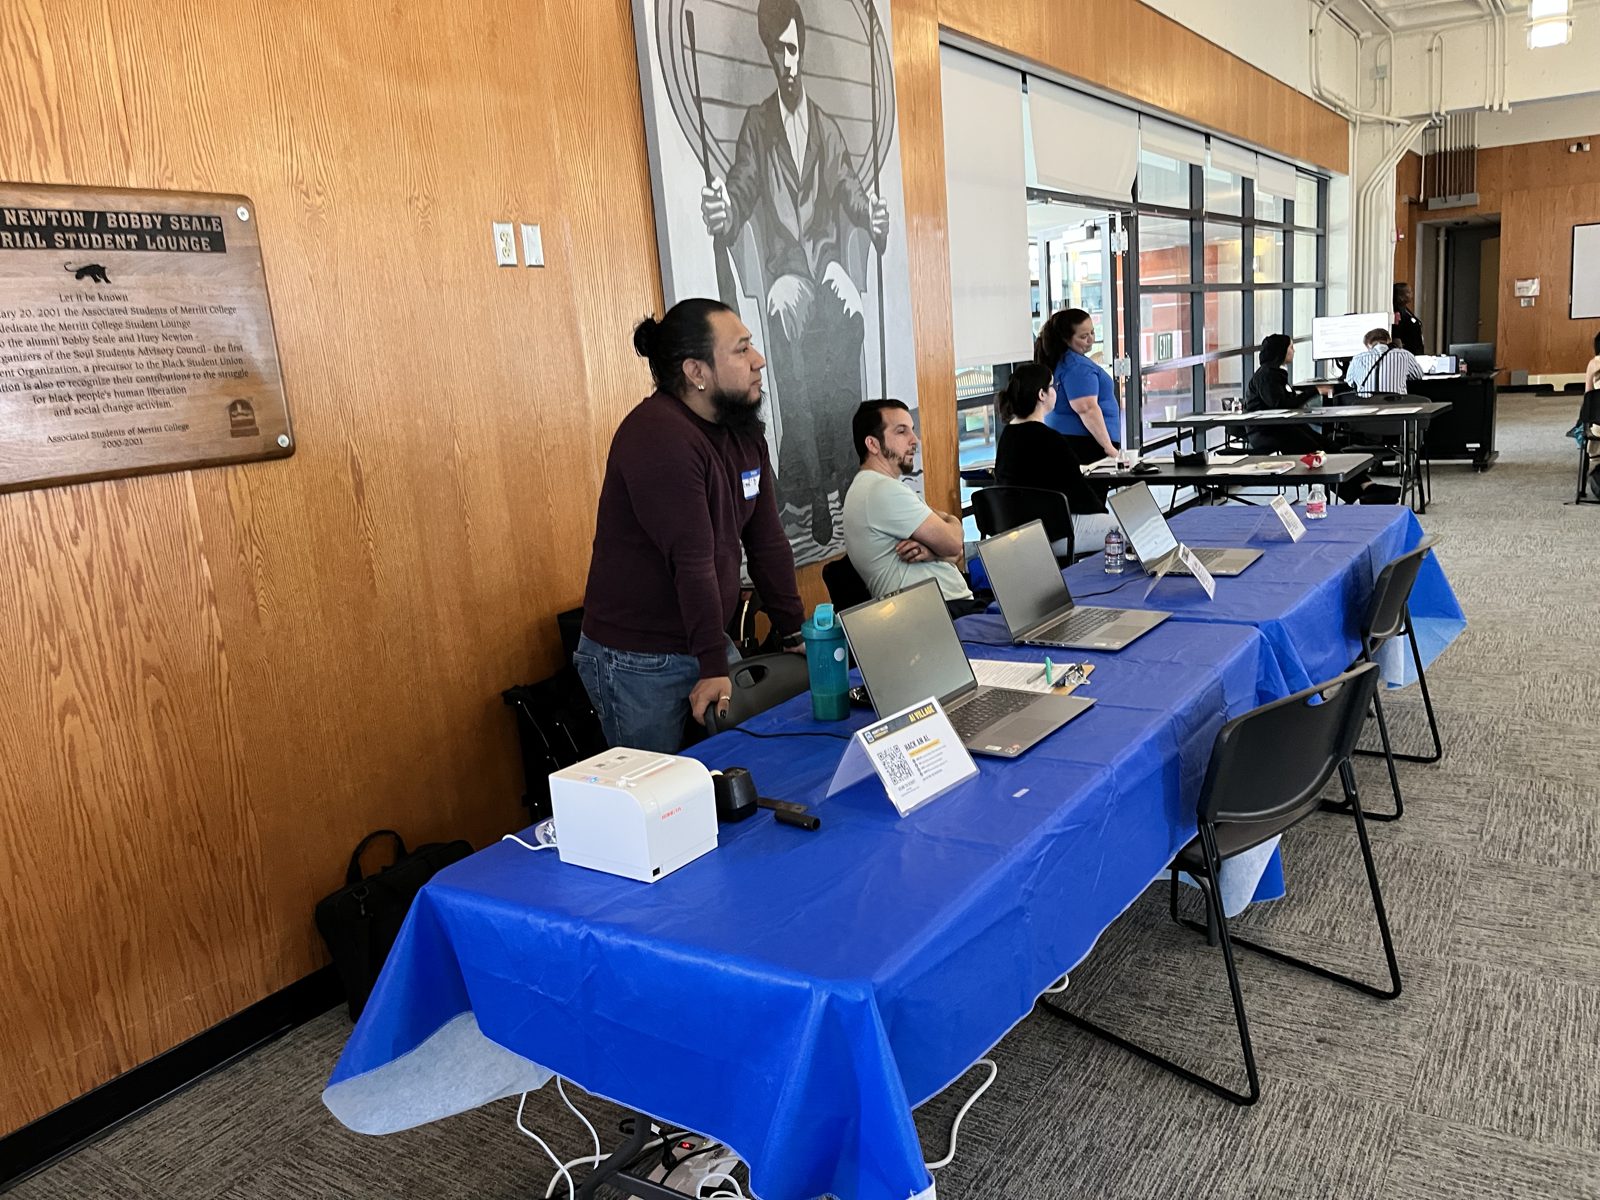
workshops. Ours was a lot smaller: three computers, a receipt printer, a TV and
a few student hosts.
The booth in the Newton/Seale Lounge: receipt printer, table tent, and three laptops for TryHackMe, the AI Labs and the CTF.
What we offered
Sign up. Students scanned the QR code on the table tent and signed up on their phone with their name, email and a hacker
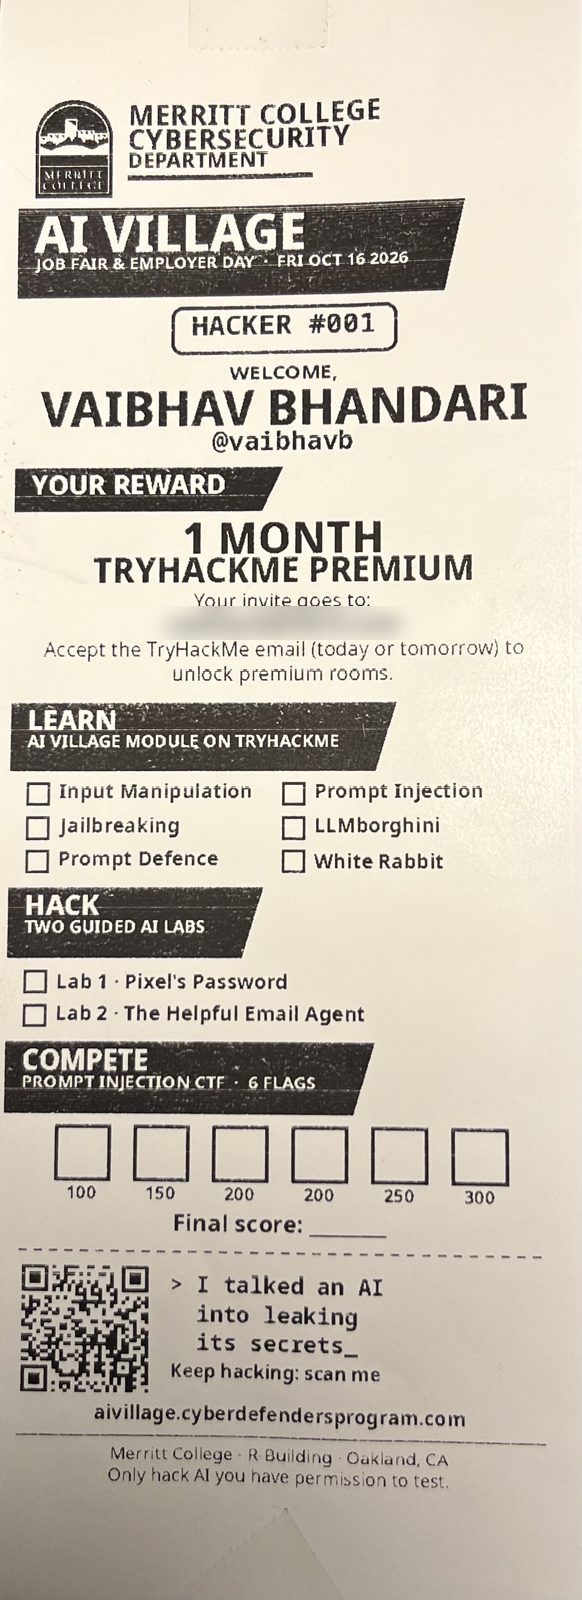
handle. A thermal receipt printer at the booth printed a souvenir receipt with their hacker number, a checklist of everything to
try, and a QR code to keep going at home.
The souvenir receipt. Students kept asking how it worked. Each one has a hacker number, the TryHackMe reward,
tick-boxes for every room and lab, six boxes for CTF flags, and a QR code to keep hacking at home.
Learn on TryHackMe. Everyone who signed up got a free month of TryHackMe Premium through the Peralta Colleges account. We put
together a custom module, AI Village @ Merritt: Hack the AI, with six rooms: Input Manipulation & Prompt Injection,
Prompt Injection, Jailbreaking, LLMborghini, Prompt Defence and White Rabbit. Invites went out the same day.
Hack in our AI Labs. We built two guided labs that run on a small server in our home lab, with an open model
(Qwen3 30B) on llama.cpp. No API bill, and nothing to install for students.
Lab 1, Pixel's Password. Get a chatbot to give up its password across three levels: no defense, told to keep it secret,
and then input and output filters. Hints on the side walk you through it.
Lab 2, The Helpful Email Agent. You can only send Priya an email. Her AI agent reads her inbox and can send mail. Win by
getting the agent to email her reset code to you. Then turn on the defenses and try again.
Compete in the CTF. Six prompt injection challenges worth 100 to 300 points: Hello Pixel, The Vault, Output Filter, Lost in
Translation, Review Summarizer (indirect injection, where you only get to write a product review) and Guardian (blocked words plus
an output filter). Every player gets their own flags, so copying a friend's doesn't work. A live scoreboard ran on the TV. The CTF
also had a backup that runs the same model on OpenRouter, in case the home server got busy. We never needed it.
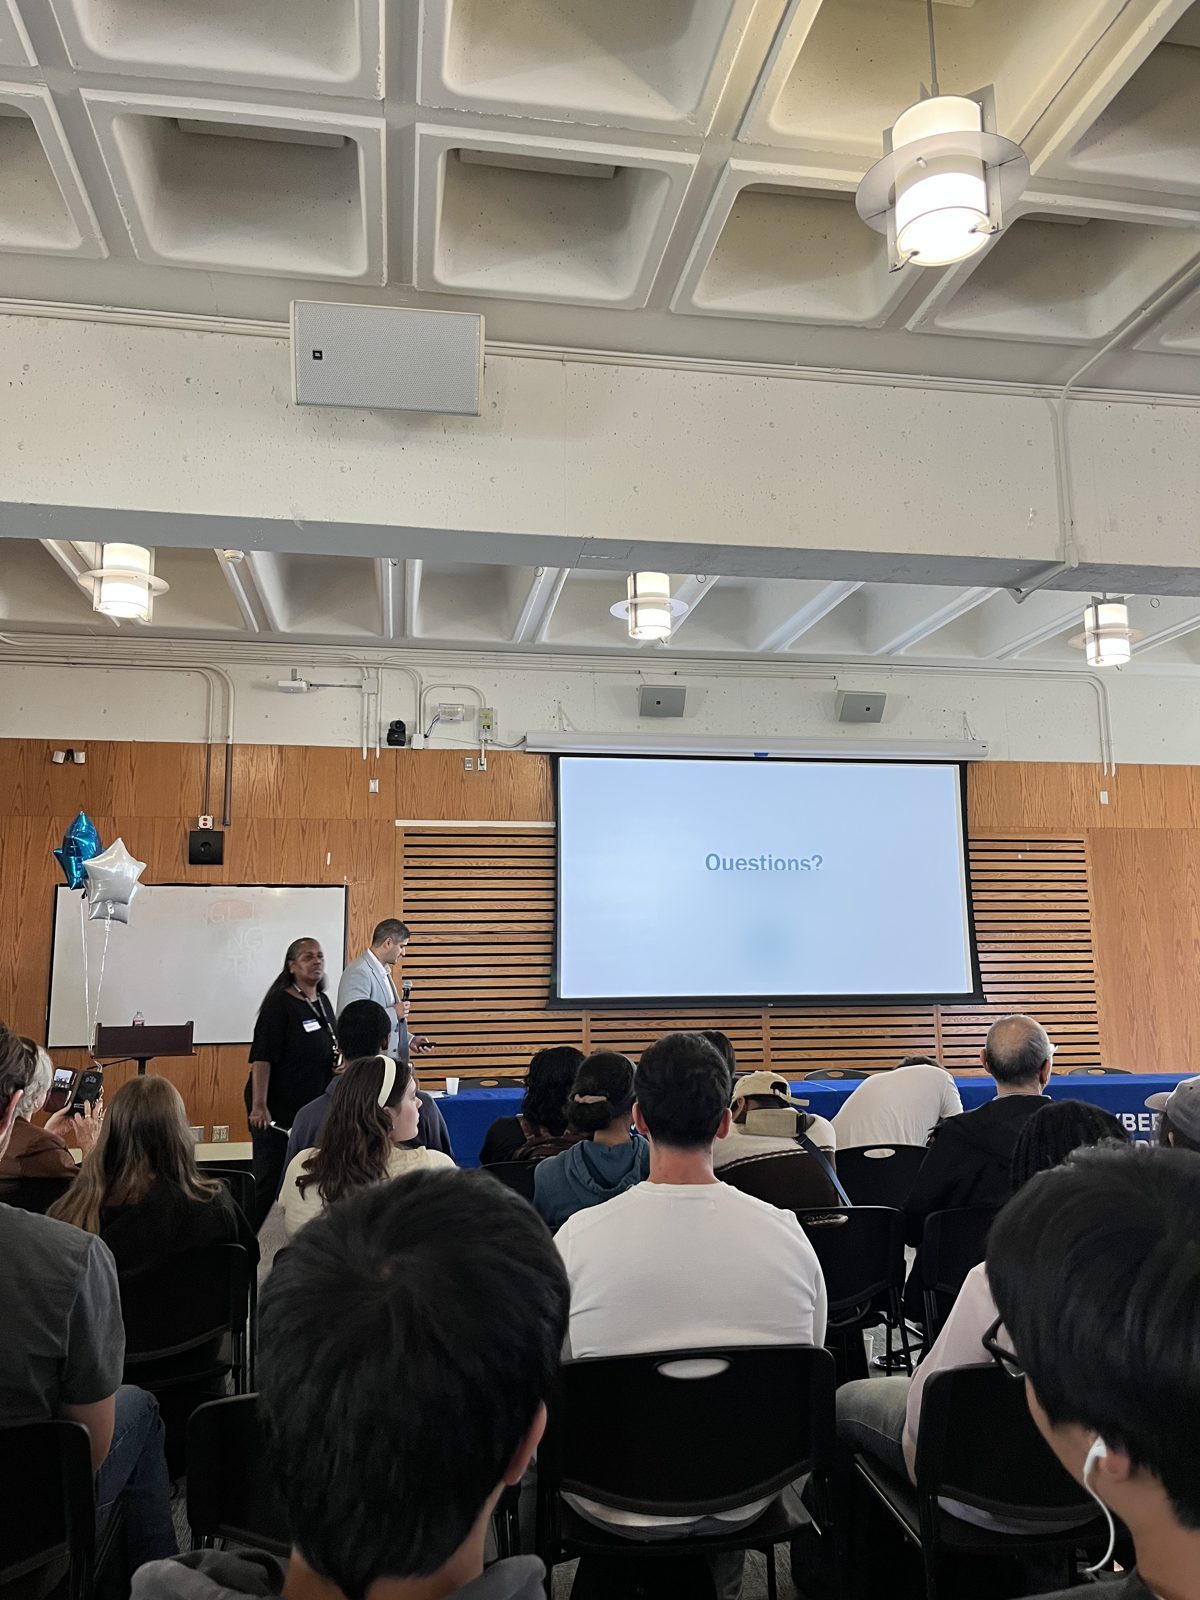
A full room for the talks at the job fair.
By the numbers
19 students signed up, and 19 TryHackMe Premium invites went out
4 students played the CTF and captured 8 flags
Top score: GNick with 450 points, then baytomwo and Amal with 250 each
About 100 messages to the CTF bots, all answered by our own server
Busiest hour: 1 pm, with 7 signups
Final scoreboard
#
Hacker
Flags
Points
1
GNick
3
450
2
baytomwo
2
250
3
Amal
2
250
4
armand
1
100
Flags by challenge
Challenge
Points
Solved by
Hello, Pixel
100
4
The Vault
150
3
Output Filter
200
1
Lost in Translation
200
0
Review Summarizer
250
0
Guardian
300
0
The live CTF site was retired after the event; this page is its record. Want to try the challenges?
Run your own copy from GitHub.
What we learned
Sign-ups and TryHackMe worked well. The CTF and labs were quieter than we hoped. Most students had a few minutes between employer
tables, not fifteen. Hello Pixel did its job: every CTF player solved it. Nobody got past Output Filter on the day, and the harder
challenges need more time than a job fair gives.
Next time we want to run short, 5-minute group demos on the big screen at set times, and give a small prize for the top score.
Use it yourself
Everything we built is on GitHub: the two labs and the CTF with its sign-up site and scoreboard.
Feel free to use it for your own class or event:
github.com/cyberdefendersprogram/aivillage.
Want an AI Village at your school or event? Get in touch.
Thank you to our student hosts, the Merritt College Cybersecurity department, TryHackMe, and everyone who stopped by.
Keep hacking, but only hack AI you have permission to test.